|
Poslao: 03 Dec 2008 13:12
|
offline
- majica
- Novi MyCity građanin

- Pridružio: 15 Feb 2006
- Poruke: 9
|
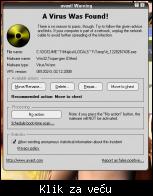
Molila bih nekog ako moze da mi pomogne da se resim ove spodobe.
Juce mi je Avast detektovao trojana i nudi mi opcije kao sto su repair, no akction, delete, move to chest.Sta god da stisnem od toga prilikom skeniranja opet ga nadje.
A kaze da je detektovan u temp.inter.files iako sam ceo taj folder izbrisala.
Sta da radim ima li neko ideju?
|
|
|
|
|
|
|
Poslao: 03 Dec 2008 13:22
|
offline
- helen1

- Anti Malware Fighter
Rank 2

- Pridružio: 27 Avg 2005
- Poruke: 8657
- Gde živiš: Novi Beograd
|
[Link mogu videti samo ulogovani korisnici]
|
|
|
|
|
|
|
Poslao: 03 Dec 2008 13:33
|
offline
- majica
- Novi MyCity građanin
- Pridružio: 15 Feb 2006
- Poruke: 9
|
Thanks Helen!
Evo odradila sam valjda kako treba
Logfile of Trend Micro HijackThis v2.0.2
Scan saved at 13:30:12, on 3.12.2008
Platform: Windows XP SP2 (WinNT 5.01.2600)
MSIE: Internet Explorer v6.00 SP2 (6.00.2900.2180)
Boot mode: Normal
Running processes:
C:\WINDOWS\System32\smss.exe
C:\WINDOWS\system32\winlogon.exe
C:\WINDOWS\system32\services.exe
C:\WINDOWS\system32\lsass.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\System32\svchost.exe
C:\Program Files\Alwil Software\Avast4\aswUpdSv.exe
C:\Program Files\Alwil Software\Avast4\ashServ.exe
C:\WINDOWS\system32\spoolsv.exe
C:\Program Files\Common Files\Apple\Mobile Device Support\bin\AppleMobileDeviceService.exe
C:\Program Files\Bonjour\mDNSResponder.exe
C:\WINDOWS\system32\nvsvc32.exe
C:\WINDOWS\system32\svchost.exe
C:\Program Files\Alwil Software\Avast4\ashMaiSv.exe
C:\Program Files\Alwil Software\Avast4\ashWebSv.exe
C:\WINDOWS\Explorer.EXE
C:\WINDOWS\Anvshell.exe
C:\WINDOWS\system32\WgaTray.exe
C:\Program Files\Elaborate Bytes\CloneCD\CloneCDTray.exe
C:\Program Files\Common Files\ACD Systems\EN\DevDetect.exe
C:\Program Files\Winamp\winampa.exe
C:\WINDOWS\system32\LVCOMSX.EXE
C:\Program Files\Common Files\Real\Update_OB\realsched.exe
C:\PROGRA~1\ALWILS~1\Avast4\ashDisp.exe
C:\WINDOWS\system32\rundll32.exe
C:\WINDOWS\system32\ctfmon.exe
C:\Program Files\Messenger\msmsgs.exe
C:\Program Files\Internet Explorer\iexplore.exe
D:\instalirani programi\Phone\Skype.exe
C:\Documents and Settings\All Users\Application Data\Skype\Plugins\Plugins\A2F36B1829EB4E69AC53989EB936C018\ScreenShot.exe
C:\Program Files\Spybot - Search & Destroy\TeaTimer.exe
C:\Program Files\Toshiba\Bluetooth Toshiba Stack\TosBtMng.exe
C:\Program Files\Common Files\Microsoft Shared\Windows Live\WLLoginProxy.exe
C:\Program Files\Toshiba\Bluetooth Toshiba Stack\TosA2dp.exe
C:\Program Files\Toshiba\Bluetooth Toshiba Stack\TosBtHsp.exe
C:\Program Files\Toshiba\Bluetooth Toshiba Stack\tosOBEX.exe
C:\Program Files\Toshiba\Bluetooth Toshiba Stack\tosBtProc.exe
D:\instalirani programi\Plugin Manager\skypePM.exe
C:\Documents and Settings\All Users\Application Data\Skype\Plugins\Plugins\903CB56BA52F42478957BE8314837A86\PamelaPCR.exe
C:\Documents and Settings\All Users\Application Data\Skype\Plugins\Plugins\61BEB79ECBDD451F9554700542EE2D92\WinampMood.exe
C:\WINDOWS\system32\wuauclt.exe
C:\Program Files\Internet Explorer\IEXPLORE.EXE
C:\Program Files\Mozilla Firefox\firefox.exe
C:\Program Files\IncrediMail\bin\IMApp.exe
C:\Documents and Settings\Majica\Desktop\Virus\TR3.exe
R0 - HKCU\Software\Microsoft\Internet Explorer\Main,Start Page = [Link mogu videti samo ulogovani korisnici]
R3 - URLSearchHook: Yahoo! Toolbar - {EF99BD32-C1FB-11D2-892F-0090271D4F88} - (no file)
R3 - URLSearchHook: SweetIM For Internet Explorer - {BC4FFE41-DE9F-46fa-B455-AAD49B9F9938} - C:\Program Files\Macrogaming\SweetIMBarForIE\toolbar.dll
O2 - BHO: AcroIEHlprObj Class - {06849E9F-C8D7-4D59-B87D-784B7D6BE0B3} - C:\Program Files\Adobe\Acrobat 7.0\ActiveX\AcroIEHelper.dll
O2 - BHO: SWEETIE Class - {1A0AADCD-3A72-4b5f-900F-E3BB5A838E2A} - C:\PROGRA~1\MACROG~1\SWEETI~1\toolbar.dll
O2 - BHO: Spybot-S&D IE Protection - {53707962-6F74-2D53-2644-206D7942484F} - C:\PROGRA~1\SPYBOT~1\SDHelper.dll
O2 - BHO: 351631 helper - {6A26574A-DD6D-4382-8C76-0DF06C478D3A} - C:\WINDOWS\system32\351631\351631.dll
O2 - BHO: (no name) - {7E853D72-626A-48EC-A868-BA8D5E23E045} - (no file)
O2 - BHO: Windows Live Sign-in Helper - {9030D464-4C02-4ABF-8ECC-5164760863C6} - C:\Program Files\Common Files\Microsoft Shared\Windows Live\WindowsLiveLogin.dll
O3 - Toolbar: SweetIM For Internet Explorer - {BC4FFE41-DE9F-46fa-B455-AAD49B9F9938} - C:\Program Files\Macrogaming\SweetIMBarForIE\toolbar.dll
O4 - HKLM\..\Run: [Anvshell] C:\WINDOWS\Anvshell.exe
O4 - HKLM\..\Run: [NvCplDaemon] RUNDLL32.EXE C:\WINDOWS\system32\NvCpl.dll,NvStartup
O4 - HKLM\..\Run: [nwiz] nwiz.exe /install
O4 - HKLM\..\Run: [ICQ Lite] "C:\Program Files\ICQLite\ICQLite.exe" -minimize
O4 - HKLM\..\Run: [CloneCDElbyCDFL] "C:\Program Files\Elaborate Bytes\CloneCD\ElbyCheck.exe" /L ElbyCDFL
O4 - HKLM\..\Run: [CloneCDTray] "C:\Program Files\Elaborate Bytes\CloneCD\CloneCDTray.exe"
O4 - HKLM\..\Run: [Device Detector] DevDetect.exe -autorun
O4 - HKLM\..\Run: [WinampAgent] C:\Program Files\Winamp\winampa.exe
O4 - HKLM\..\Run: [LVCOMSX] C:\WINDOWS\system32\LVCOMSX.EXE
O4 - HKLM\..\Run: [LogitechVideoRepair] C:\Program Files\Logitech\Video\ISStart.exe
O4 - HKLM\..\Run: [LogitechVideoTray] C:\Program Files\Logitech\Video\LogiTray.exe
O4 - HKLM\..\Run: [My Web Search Bar] rundll32 C:\PROGRA~1\MYWEBS~1\bar\1.bin\MWSBAR.DLL,S
O4 - HKLM\..\Run: [TkBellExe] "C:\Program Files\Common Files\Real\Update_OB\realsched.exe" -osboot
O4 - HKLM\..\Run: [MyWebSearch Email Plugin] C:\PROGRA~1\MYWEBS~1\bar\1.bin\mwsoemon.exe
O4 - HKLM\..\Run: [avast!] C:\PROGRA~1\ALWILS~1\Avast4\ashDisp.exe
O4 - HKLM\..\Run: [BluetoothAuthenticationAgent] rundll32.exe bthprops.cpl,,BluetoothAuthenticationAgent
O4 - HKLM\..\Run: [AppleSyncNotifier] C:\Program Files\Common Files\Apple\Mobile Device Support\bin\AppleSyncNotifier.exe
O4 - HKLM\..\Run: [QuickTime Task] "C:\Program Files\QuickTime\qttask.exe" -atboottime
O4 - HKLM\..\Run: [sysftray2] C:\windows\bolivar27.exe
O4 - HKCU\..\Run: [CTFMON.EXE] C:\WINDOWS\system32\ctfmon.exe
O4 - HKCU\..\Run: [Free Download Manager] C:\Program Files\Free Download Manager\fdm.exe -autorun
O4 - HKCU\..\Run: [MSMSGS] "C:\Program Files\Messenger\msmsgs.exe" /background
O4 - HKCU\..\Run: [Skype] "D:\instalirani programi\Phone\Skype.exe" /nosplash /minimized
O4 - HKCU\..\Run: [IncrediMail] C:\Program Files\IncrediMail\bin\IncMail.exe /c
O4 - HKCU\..\Run: [Magentic] C:\PROGRA~1\Magentic\bin\Magentic.exe /c
O4 - HKCU\..\Run: [LogitechSoftwareUpdate] "C:\Program Files\Logitech\Video\ManifestEngine.exe" boot
O4 - HKCU\..\Run: [ScreenShot.exe] "C:\Documents and Settings\All Users\Application Data\Skype\Plugins\Plugins\A2F36B1829EB4E69AC53989EB936C018\ScreenShot.exe" /startup
O4 - HKCU\..\Run: [SkypeCryptoChat] "C:\Documents and Settings\Majica\Local Settings\Apps\2.0\A14HK237.D87\K6L4CC2Y.5L1\lfcr..tion_5ec75c53587d555c_0001.0000_24dda2dd7ec46018\LFCryptoChat4Skype.exe" /minimized
O4 - HKCU\..\Run: [SpybotSD TeaTimer] C:\Program Files\Spybot - Search & Destroy\TeaTimer.exe
O4 - HKUS\S-1-5-19\..\Run: [CTFMON.EXE] C:\WINDOWS\system32\CTFMON.EXE (User 'LOCAL SERVICE')
O4 - HKUS\S-1-5-20\..\Run: [CTFMON.EXE] C:\WINDOWS\system32\CTFMON.EXE (User 'NETWORK SERVICE')
O4 - HKUS\S-1-5-18\..\Run: [CTFMON.EXE] C:\WINDOWS\system32\CTFMON.EXE (User 'SYSTEM')
O4 - HKUS\.DEFAULT\..\Run: [CTFMON.EXE] C:\WINDOWS\system32\CTFMON.EXE (User 'Default user')
O4 - Global Startup: Bluetooth Manager.lnk = ?
O8 - Extra context menu item: &Search - [Link mogu videti samo ulogovani korisnici]
O8 - Extra context menu item: E&xport to Microsoft Excel - [Link mogu videti samo ulogovani korisnici]\PROGRA~1\MICROS~2\OFFICE11\EXCEL.EXE/3000
O9 - Extra button: Research - {92780B25-18CC-41C8-B9BE-3C9C571A8263} - C:\PROGRA~1\MICROS~2\OFFICE11\REFIEBAR.DLL
O9 - Extra button: (no name) - {DFB852A3-47F8-48C4-A200-58CAB36FD2A2} - C:\PROGRA~1\SPYBOT~1\SDHelper.dll
O9 - Extra 'Tools' menuitem: Spybot - Search & Destroy Configuration - {DFB852A3-47F8-48C4-A200-58CAB36FD2A2} - C:\PROGRA~1\SPYBOT~1\SDHelper.dll
O9 - Extra button: Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O9 - Extra 'Tools' menuitem: Windows Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O16 - DPF: ConferenceRoom Java Client - [Link mogu videti samo ulogovani korisnici]
O16 - DPF: {17492023-C23A-453E-A040-C7C580BBF700} (Windows Genuine Advantage Validation Tool) - [Link mogu videti samo ulogovani korisnici]
O16 - DPF: {30528230-99f7-4bb4-88d8-fa1d4f56a2ab} (YInstStarter Class) - C:\Program Files\Yahoo!\Common\yinsthelper.dll
O17 - HKLM\System\CCS\Services\Tcpip\..\{2CA7FDFE-46E6-4712-89A5-E8F4C4728E61}: NameServer = 195.66.160.1,195.66.160.2
O17 - HKLM\System\CCS\Services\Tcpip\..\{FE624B93-FA28-49B7-8D4D-7352E9FF9A75}: NameServer = 195.66.160.1 195.66.160.2
O18 - Protocol: skype4com - {FFC8B962-9B40-4DFF-9458-1830C7DD7F5D} - C:\PROGRA~1\COMMON~1\Skype\SKYPE4~1.DLL
O23 - Service: Apple Mobile Device - Apple Inc. - C:\Program Files\Common Files\Apple\Mobile Device Support\bin\AppleMobileDeviceService.exe
O23 - Service: avast! iAVS4 Control Service (aswUpdSv) - ALWIL Software - C:\Program Files\Alwil Software\Avast4\aswUpdSv.exe
O23 - Service: avast! Antivirus - ALWIL Software - C:\Program Files\Alwil Software\Avast4\ashServ.exe
O23 - Service: avast! Mail Scanner - ALWIL Software - C:\Program Files\Alwil Software\Avast4\ashMaiSv.exe
O23 - Service: avast! Web Scanner - ALWIL Software - C:\Program Files\Alwil Software\Avast4\ashWebSv.exe
O23 - Service: Bonjour Service - Apple Inc. - C:\Program Files\Bonjour\mDNSResponder.exe
O23 - Service: Bonjour Service (Bonjour Service) - Unknown owner - C:\Program Files\tinyproxy\tinyproxy.exe (file missing)
O23 - Service: InstallDriver Table Manager (IDriverT) - Macrovision Corporation - C:\Program Files\Common Files\InstallShield\Driver\11\Intel 32\IDriverT.exe
O23 - Service: Network Location Awareness (NLA) (Nla) - Unknown owner - C:\Program Files\tinyproxy\tinyproxy.exe (file missing)
O23 - Service: NVIDIA Driver Helper Service (NVSvc) - NVIDIA Corporation - C:\WINDOWS\system32\nvsvc32.exe
O24 - Desktop Component 0: (no name) - [Link mogu videti samo ulogovani korisnici]
--
End of file - 9588 bytes
|
|
|
|
|
|
|
Poslao: 03 Dec 2008 13:40
|
offline
- helen1
- Anti Malware Fighter
Rank 2
- Pridružio: 27 Avg 2005
- Poruke: 8657
- Gde živiš: Novi Beograd
|
Zovem se Dusan, helen1 mi je "umetnicko ime".
Uradi sledece:
Klikni desnim tasterom miša na avast! ikonicu (  ) u donjem, desnom uglu ekrana i izaberi Stop OnAccess Protection.
Napomena: Ne zaboravi da uključiš ovu opciju po završetku čišćenja.
------------------------------------
Skini ComboFix sa jedne od sledecih adresa na Desktop:
[Link mogu videti samo ulogovani korisnici]
[Link mogu videti samo ulogovani korisnici]
[Link mogu videti samo ulogovani korisnici]
Startuj ga i ne diraj prozor programa dok skenira.
Sledi uputstva na ekranu. Kada zavrsi pojavice se log (C:\ComboFix.txt) koji ces nam ovde iskopirati.
|
|
|
|
|
|
|
Poslao: 03 Dec 2008 18:17
|
offline
- majica
- Novi MyCity građanin
- Pridružio: 15 Feb 2006
- Poruke: 9
|
Ok Dusane :O)
evo sam odradila sta si mi rekao...nadam se da je dobro.
ComboFix 08-12-01.03 - Majica 2008-12-03 13:46:05.1 - NTFSx86
Running from: c:\documents and settings\Majica\Desktop\ComboFix.exe
* Created a new restore point
.
((((((((((((((((((((((((((((((((((((((( Other Deletions )))))))))))))))))))))))))))))))))))))))))))))))))
.
c:\documents and settings\Majica\Application Data\.#
c:\documents and settings\Majica\Application Data\FunWebProducts
c:\program files\MyWebSearch
c:\program files\MyWebSearch\bar\1.bin\MWSOEMON.EXE
c:\program files\TinyProxy
c:\windows\bolivar27.exe
c:\windows\fmark2.dat
c:\windows\system32\351631
c:\windows\system32\351631\351631.dll
.
((((((((((((((((((((((((( Files Created from 2008-11-03 to 2008-12-03 )))))))))))))))))))))))))))))))
.
2008-12-02 23:31 . 2008-12-03 01:41 <DIR> d-------- c:\program files\Spybot - Search & Destroy
2008-12-02 22:40 . 2008-12-03 12:31 915 ---h----- c:\windows\f49f4d98.dat
2008-12-02 22:13 . 2008-12-03 12:29 1 ---h----- c:\windows\f49f4daa.dat
2008-12-02 22:13 . 2008-12-02 22:13 1 ---h----- c:\windows\bemark2.dat
2008-11-28 13:37 . 2008-11-28 13:37 <DIR> d-------- c:\documents and settings\All Users\Application Data\InterAction studios
2008-11-25 00:40 . 2008-11-25 00:40 32 --a------ c:\documents and settings\All Users\Application Data\ezsid.dat
2008-11-10 22:26 . 2008-11-10 22:26 <DIR> d-------- c:\program files\Skype
.
(((((((((((((((((((((((((((((((((((((((( Find3M Report ))))))))))))))))))))))))))))))))))))))))))))))))))))
.
2008-12-03 12:23 --------- d-----w c:\documents and settings\Majica\Application Data\Skype
2008-12-03 11:24 --------- d-----w c:\documents and settings\Majica\Application Data\WizzTones
2008-12-03 11:23 --------- d-----w c:\documents and settings\Majica\Application Data\skypePM
2008-12-03 00:42 --------- d-----w c:\documents and settings\All Users\Application Data\Spybot - Search & Destroy
2008-11-28 13:12 --------- d-----w c:\program files\Chicken Invaders
2008-10-24 11:10 453,632 ----a-w c:\windows\system32\drivers\mrxsmb.sys
2008-10-20 10:57 180,064 ----a-w c:\windows\system32\WinVd32.sys
2008-10-20 10:57 16,384 ----a-w c:\windows\system32\WinFl32.sys
2008-10-18 10:59 --------- d--h--w c:\program files\InstallShield Installation Information
2008-10-17 15:20 --------- d-----w c:\documents and settings\Majica\Application Data\ScreenShot
2008-10-17 14:18 --------- d-----w c:\documents and settings\All Users\Application Data\InstallShield
2008-10-17 14:17 --------- d-----w c:\program files\Common Files\InstallShield
2008-10-16 13:13 202,776 ----a-w c:\windows\system32\wuweb.dll
2008-10-16 13:13 1,809,944 ----a-w c:\windows\system32\wuaueng.dll
2008-10-16 13:12 561,688 ----a-w c:\windows\system32\wuapi.dll
2008-10-16 13:12 323,608 ----a-w c:\windows\system32\wucltui.dll
2008-10-16 13:09 92,696 ----a-w c:\windows\system32\cdm.dll
2008-10-16 13:09 51,224 ----a-w c:\windows\system32\wuauclt.exe
2008-10-16 13:09 43,544 ----a-w c:\windows\system32\wups2.dll
2008-10-16 13:08 34,328 ----a-w c:\windows\system32\wups.dll
2008-10-16 13:06 268,648 ----a-w c:\windows\system32\mucltui.dll
2008-10-16 13:06 208,744 ----a-w c:\windows\system32\muweb.dll
2008-10-13 12:41 --------- d-----w c:\documents and settings\Majica\Application Data\Winamp
2008-09-15 11:57 1,846,016 ------w c:\windows\system32\win32k.sys
2008-09-04 16:42 1,106,944 ----a-w c:\windows\system32\msxml3.dll
2007-11-05 16:34 439,208 ----a-w c:\documents and settings\Majica\setup.exe
2006-03-22 00:50 1,980,719 -c--a-w c:\documents and settings\My Documents\yurecnik11.exe
2006-02-16 02:00 5,598,928 -c--a-w c:\documents and settings\My Documents\winamp52_0440_beta_full.exe
.
((((((((((((((((((((((((((((((((((((( Reg Loading Points ))))))))))))))))))))))))))))))))))))))))))))))))))
.
.
*Note* empty entries & legit default entries are not shown
REGEDIT4
[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"CTFMON.EXE"="c:\windows\system32\ctfmon.exe" [2004-08-04 15360]
"MSMSGS"="c:\program files\Messenger\msmsgs.exe" [2004-10-13 1694208]
"Skype"="d:\instalirani programi\Phone\Skype.exe" [2008-09-23 21755688]
"IncrediMail"="c:\program files\IncrediMail\bin\IncMail.exe" [2008-07-24 243072]
"ScreenShot.exe"="c:\documents and settings\All Users\Application Data\Skype\Plugins\Plugins\A2F36B1829EB4E69AC53989EB936C018\ScreenShot.exe" [2008-10-17 483328]
"SpybotSD TeaTimer"="c:\program files\Spybot - Search & Destroy\TeaTimer.exe" [2008-09-16 1833296]
[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"Anvshell"="c:\windows\Anvshell.exe" [2002-10-22 331776]
"NvCplDaemon"="c:\windows\system32\NvCpl.dll" [2003-05-02 4640768]
"CloneCDElbyCDFL"="c:\program files\Elaborate Bytes\CloneCD\ElbyCheck.exe" [2002-11-02 45056]
"CloneCDTray"="c:\program files\Elaborate Bytes\CloneCD\CloneCDTray.exe" [2002-12-02 73728]
"WinampAgent"="c:\program files\Winamp\winampa.exe" [2006-11-21 35328]
"LVCOMSX"="c:\windows\system32\LVCOMSX.EXE" [2004-10-08 221184]
"TkBellExe"="c:\program files\Common Files\Real\Update_OB\realsched.exe" [2007-05-06 185784]
"avast!"="c:\progra~1\ALWILS~1\Avast4\ashDisp.exe" [2008-11-26 81000]
"AppleSyncNotifier"="c:\program files\Common Files\Apple\Mobile Device Support\bin\AppleSyncNotifier.exe" [2008-07-22 116040]
"QuickTime Task"="c:\program files\QuickTime\qttask.exe" [2008-05-27 413696]
"nwiz"="nwiz.exe" [2003-05-02 c:\windows\system32\nwiz.exe]
"BluetoothAuthenticationAgent"="bthprops.cpl" [2004-08-04 c:\windows\system32\bthprops.cpl]
[HKEY_USERS\.DEFAULT\Software\Microsoft\Windows\CurrentVersion\Run]
"CTFMON.EXE"="c:\windows\system32\CTFMON.EXE" [2004-08-04 15360]
[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\AuthorizedApplications\List]
"%windir%\\system32\\sessmgr.exe"=
"c:\\Program Files\\IncrediMail\\bin\\IMApp.exe"=
"c:\\Program Files\\IncrediMail\\bin\\IncMail.exe"=
"c:\\Program Files\\IncrediMail\\bin\\ImpCnt.exe"=
"d:\\instalirani programi\\DC++\\DCPlusPlus.exe"=
"c:\\WINDOWS\\system32\\dpvsetup.exe"=
"c:\\WINDOWS\\system32\\mcoinstall.exe"=
"c:\\Program Files\\Windows Live\\Messenger\\msnmsgr.exe"=
"c:\\Program Files\\Windows Live\\Messenger\\livecall.exe"=
"c:\\Program Files\\Bonjour\\mDNSResponder.exe"=
"d:\\instalirani programi\\Phone\\Skype.exe"=
[HKEY_CURRENT_USER\software\microsoft\windows\currentversion\explorer\mountpoints2\{2a35c714-09e2-11dd-9794-000c6ef8e692}]
\Shell\AutoRun\command - F:\EXPLORER.EXE
\Shell\explore\Command - F:\EXPLORER.EXE
\Shell\open\Command - F:\EXPLORER.EXE
[HKEY_CURRENT_USER\software\microsoft\windows\currentversion\explorer\mountpoints2\{a325729c-1b53-11db-a99d-000c6ef8e692}]
\Shell\AutoRun\command - c:\windows\system32\RunDLL32.EXE Shell32.DLL,ShellExec_RunDLL Setup.pif
*Newly Created Service* - PROCEXP90
.
Contents of the 'Scheduled Tasks' folder
2008-11-26 c:\windows\Tasks\AppleSoftwareUpdate.job
- c:\program files\Apple Software Update\SoftwareUpdate.exe [2008-04-11 16:57]
.
- - - - ORPHANS REMOVED - - - -
BHO-{6A26574A-DD6D-4382-8C76-0DF06C478D3A} - c:\windows\system32\351631\351631.dll
HKCU-Run-Free Download Manager - c:\program files\Free Download Manager\fdm.exe
HKCU-Run-Magentic - c:\progra~1\Magentic\bin\Magentic.exe
HKCU-Run-LogitechSoftwareUpdate - c:\program files\Logitech\Video\ManifestEngine.exe
HKCU-Run-SkypeCryptoChat - c:\documents and settings\Majica\Local Settings\Apps\2.0\A14HK237.D87\K6L4CC2Y.5L1\lfcr..tion_5ec75c53587d555c_0001.0000_24dda2dd7ec46018\LFCryptoChat4Skype.exe
HKLM-Run-ICQ Lite - c:\program files\ICQLite\ICQLite.exe
HKLM-Run-LogitechVideoRepair - c:\program files\Logitech\Video\ISStart.exe
HKLM-Run-LogitechVideoTray - c:\program files\Logitech\Video\LogiTray.exe
HKLM-Run-Device Detector - DevDetect.exe
.
------- Supplementary Scan -------
.
FireFox -: Profile - c:\documents and settings\Majica\Application Data\Mozilla\Firefox\Profiles\kqh5r0kl.default\
FF -: plugin - c:\program files\Adobe\Acrobat 7.0\Reader\browser\nppdf32.dll
FF -: plugin - c:\program files\Panda Security\TotalScan\npwrapper.dll
.
**************************************************************************
catchme 0.3.1367 W2K/XP/Vista - rootkit/stealth malware detector by Gmer, [Link mogu videti samo ulogovani korisnici]
Rootkit scan 2008-12-03 13:47:21
Windows 5.1.2600 Service Pack 2 NTFS
scanning hidden processes ...
scanning hidden autostart entries ...
scanning hidden files ...
**************************************************************************
.
Completion time: 2008-12-03 13:49:15
ComboFix-quarantined-files.txt 2008-12-03 12:47:58
Pre-Run: 2.065.846.272 bytes free
Post-Run: 2,107,265,024 bytes free
WindowsXP-KB310994-SP2-Pro-BootDisk-ENU.exe
[boot loader]
timeout=2
default=multi(0)disk(0)rdisk(0)partition(1)\WINDOWS
[operating systems]
c:\cmdcons\BOOTSECT.DAT="Microsoft Windows Recovery Console" /cmdcons
multi(0)disk(0)rdisk(0)partition(1)\WINDOWS="Microsoft Windows XP Professional" /noexecute=optin /fastdetect
145 --- E O F --- 2008-11-12 02:03:56
Dopuna: 03 Dec 2008 18:17
Sta dalje ?
|
|
|
|
|
|
|
Poslao: 04 Dec 2008 07:54
|
offline
- helen1
- Anti Malware Fighter
Rank 2
- Pridružio: 27 Avg 2005
- Poruke: 8657
- Gde živiš: Novi Beograd
|
Uploaduj mi sledece fajlove:
c:\windows\system32\WinVd32.sys
c:\windows\system32\WinFl32.sys
c:\documents and settings\Majica\setup.exe
preko sledeceg linka:
[Link mogu videti samo ulogovani korisnici]
|
|
|
|
|
|
|
|
|
Poslao: 05 Dec 2008 11:03
|
offline
- helen1
- Anti Malware Fighter
Rank 2
- Pridružio: 27 Avg 2005
- Poruke: 8657
- Gde živiš: Novi Beograd
|
Sad cekas da ti se ja sutra javim ovde u temu. Jer mi kod kuce jos ne radi net.
Dopuna: 05 Dec 2008 11:03
Ponovo iskljuci Antivirus i uradi sledece:
Otvoriti Notepad i iskopirati sledeci tekst:
File::


c:\windows\f49f4d98.dat


c:\windows\f49f4daa.dat


c:\windows\bemark2.dat
Snimiti na Desktop fajl iz Notepada kao "CFScript"

Prevuci snimljeni skript/tekst na ComboFix ikonicu kao na slici.
Postaviti u sledecoj poruci log koji bude bio napravljen na kraju ciscenja/skeniranja.
|
|
|
|
|
|
|
Poslao: 05 Dec 2008 11:39
|
offline
- majica
- Novi MyCity građanin
- Pridružio: 15 Feb 2006
- Poruke: 9
|
Evo ga:
ComboFix 08-12-01.03 - Majica 2008-12-05 11:33:33.2 - NTFSx86
Running from: c:\documents and settings\Majica\Desktop\ComboFix.exe
Command switches used :: c:\documents and settings\Majica\Desktop\CFScript.txt
* Created a new restore point
FILE ::
c:\windows\bemark2.dat
c:\windows\f49f4d98.dat
c:\windows\f49f4daa.dat
.
((((((((((((((((((((((((((((((((((((((( Other Deletions )))))))))))))))))))))))))))))))))))))))))))))))))
.
c:\windows\bemark2.dat
c:\windows\f49f4d98.dat
c:\windows\f49f4daa.dat
.
((((((((((((((((((((((((( Files Created from 2008-11-05 to 2008-12-05 )))))))))))))))))))))))))))))))
.
2008-12-02 23:31 . 2008-12-03 01:41 <DIR> d-------- c:\program files\Spybot - Search & Destroy
2008-11-28 13:37 . 2008-11-28 13:37 <DIR> d-------- c:\documents and settings\All Users\Application Data\InterAction studios
2008-11-25 00:40 . 2008-11-25 00:40 32 --a------ c:\documents and settings\All Users\Application Data\ezsid.dat
2008-11-10 22:26 . 2008-11-10 22:26 <DIR> d-------- c:\program files\Skype
.
(((((((((((((((((((((((((((((((((((((((( Find3M Report ))))))))))))))))))))))))))))))))))))))))))))))))))))
.
2008-12-05 10:36 --------- d-----w c:\documents and settings\Majica\Application Data\Skype
2008-12-05 07:07 --------- d-----w c:\documents and settings\Majica\Application Data\skypePM
2008-12-03 19:28 --------- d-----w c:\documents and settings\Majica\Application Data\WizzTones
2008-12-03 00:42 --------- d-----w c:\documents and settings\All Users\Application Data\Spybot - Search & Destroy
2008-11-28 13:12 --------- d-----w c:\program files\Chicken Invaders
2008-10-24 11:10 453,632 ----a-w c:\windows\system32\drivers\mrxsmb.sys
2008-10-20 10:57 180,064 ----a-w c:\windows\system32\WinVd32.sys
2008-10-20 10:57 16,384 ----a-w c:\windows\system32\WinFl32.sys
2008-10-18 10:59 --------- d--h--w c:\program files\InstallShield Installation Information
2008-10-17 15:20 --------- d-----w c:\documents and settings\Majica\Application Data\ScreenShot
2008-10-17 14:18 --------- d-----w c:\documents and settings\All Users\Application Data\InstallShield
2008-10-17 14:17 --------- d-----w c:\program files\Common Files\InstallShield
2008-10-16 13:13 202,776 ----a-w c:\windows\system32\wuweb.dll
2008-10-16 13:13 1,809,944 ----a-w c:\windows\system32\wuaueng.dll
2008-10-16 13:12 561,688 ----a-w c:\windows\system32\wuapi.dll
2008-10-16 13:12 323,608 ----a-w c:\windows\system32\wucltui.dll
2008-10-16 13:09 92,696 ----a-w c:\windows\system32\cdm.dll
2008-10-16 13:09 51,224 ----a-w c:\windows\system32\wuauclt.exe
2008-10-16 13:09 43,544 ----a-w c:\windows\system32\wups2.dll
2008-10-16 13:08 34,328 ----a-w c:\windows\system32\wups.dll
2008-10-16 13:06 268,648 ----a-w c:\windows\system32\mucltui.dll
2008-10-16 13:06 208,744 ----a-w c:\windows\system32\muweb.dll
2008-10-13 12:41 --------- d-----w c:\documents and settings\Majica\Application Data\Winamp
2008-09-15 11:57 1,846,016 ------w c:\windows\system32\win32k.sys
2007-11-05 16:34 439,208 ----a-w c:\documents and settings\Majica\setup.exe
2006-03-22 00:50 1,980,719 -c--a-w c:\documents and settings\My Documents\yurecnik11.exe
2006-02-16 02:00 5,598,928 -c--a-w c:\documents and settings\My Documents\winamp52_0440_beta_full.exe
.
((((((((((((((((((((((((((((((((((((( Reg Loading Points ))))))))))))))))))))))))))))))))))))))))))))))))))
.
.
*Note* empty entries & legit default entries are not shown
REGEDIT4
[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"CTFMON.EXE"="c:\windows\system32\ctfmon.exe" [2004-08-04 15360]
"MSMSGS"="c:\program files\Messenger\msmsgs.exe" [2004-10-13 1694208]
"Skype"="d:\instalirani programi\Phone\Skype.exe" [2008-09-23 21755688]
"IncrediMail"="c:\program files\IncrediMail\bin\IncMail.exe" [2008-07-24 243072]
"ScreenShot.exe"="c:\documents and settings\All Users\Application Data\Skype\Plugins\Plugins\A2F36B1829EB4E69AC53989EB936C018\ScreenShot.exe" [2008-10-17 483328]
"SpybotSD TeaTimer"="c:\program files\Spybot - Search & Destroy\TeaTimer.exe" [2008-09-16 1833296]
[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"Anvshell"="c:\windows\Anvshell.exe" [2002-10-22 331776]
"NvCplDaemon"="c:\windows\system32\NvCpl.dll" [2003-05-02 4640768]
"CloneCDElbyCDFL"="c:\program files\Elaborate Bytes\CloneCD\ElbyCheck.exe" [2002-11-02 45056]
"CloneCDTray"="c:\program files\Elaborate Bytes\CloneCD\CloneCDTray.exe" [2002-12-02 73728]
"WinampAgent"="c:\program files\Winamp\winampa.exe" [2006-11-21 35328]
"LVCOMSX"="c:\windows\system32\LVCOMSX.EXE" [2004-10-08 221184]
"TkBellExe"="c:\program files\Common Files\Real\Update_OB\realsched.exe" [2007-05-06 185784]
"avast!"="c:\progra~1\ALWILS~1\Avast4\ashDisp.exe" [2008-11-26 81000]
"AppleSyncNotifier"="c:\program files\Common Files\Apple\Mobile Device Support\bin\AppleSyncNotifier.exe" [2008-07-22 116040]
"QuickTime Task"="c:\program files\QuickTime\qttask.exe" [2008-05-27 413696]
"nwiz"="nwiz.exe" [2003-05-02 c:\windows\system32\nwiz.exe]
"BluetoothAuthenticationAgent"="bthprops.cpl" [2004-08-04 c:\windows\system32\bthprops.cpl]
[HKEY_USERS\.DEFAULT\Software\Microsoft\Windows\CurrentVersion\Run]
"CTFMON.EXE"="c:\windows\system32\CTFMON.EXE" [2004-08-04 15360]
[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\AuthorizedApplications\List]
"%windir%\\system32\\sessmgr.exe"=
"c:\\Program Files\\IncrediMail\\bin\\IMApp.exe"=
"c:\\Program Files\\IncrediMail\\bin\\IncMail.exe"=
"c:\\Program Files\\IncrediMail\\bin\\ImpCnt.exe"=
"d:\\instalirani programi\\DC++\\DCPlusPlus.exe"=
"c:\\WINDOWS\\system32\\dpvsetup.exe"=
"c:\\WINDOWS\\system32\\mcoinstall.exe"=
"c:\\Program Files\\Windows Live\\Messenger\\msnmsgr.exe"=
"c:\\Program Files\\Windows Live\\Messenger\\livecall.exe"=
"c:\\Program Files\\Bonjour\\mDNSResponder.exe"=
"d:\\instalirani programi\\Phone\\Skype.exe"=
[HKEY_CURRENT_USER\software\microsoft\windows\currentversion\explorer\mountpoints2\{2a35c714-09e2-11dd-9794-000c6ef8e692}]
\Shell\AutoRun\command - F:\EXPLORER.EXE
\Shell\explore\Command - F:\EXPLORER.EXE
\Shell\open\Command - F:\EXPLORER.EXE
[HKEY_CURRENT_USER\software\microsoft\windows\currentversion\explorer\mountpoints2\{a325729c-1b53-11db-a99d-000c6ef8e692}]
\Shell\AutoRun\command - c:\windows\system32\RunDLL32.EXE Shell32.DLL,ShellExec_RunDLL Setup.pif
.
Contents of the 'Scheduled Tasks' folder
2008-12-03 c:\windows\Tasks\AppleSoftwareUpdate.job
- c:\program files\Apple Software Update\SoftwareUpdate.exe [2008-04-11 16:57]
.
**************************************************************************
catchme 0.3.1367 W2K/XP/Vista - rootkit/stealth malware detector by Gmer, [Link mogu videti samo ulogovani korisnici]
Rootkit scan 2008-12-05 11:36:10
Windows 5.1.2600 Service Pack 2 NTFS
scanning hidden processes ...
scanning hidden autostart entries ...
scanning hidden files ...
**************************************************************************
.
Completion time: 2008-12-05 11:38:03
ComboFix-quarantined-files.txt 2008-12-05 10:36:45
ComboFix2.txt 2008-12-03 12:49:16
Pre-Run: 2.054.651.904 bytes free
Post-Run: 2,047,594,496 bytes free
116 --- E O F --- 2008-11-12 02:03:56
|
|
|
|
|
|
|
Poslao: 06 Dec 2008 10:29
|
offline
- helen1
- Anti Malware Fighter
Rank 2
- Pridružio: 27 Avg 2005
- Poruke: 8657
- Gde živiš: Novi Beograd
|
Zdravo,
kakvo je sad stanje?
Uradi sledece:
Skini sledeci program - [Link mogu videti samo ulogovani korisnici]
- startuj ga i odaberi opciju Auto block
- ubaci USB stick u komp i sacekaj koji sekund (recimo 5-10 sekundi)
- program je sada uradio analizu sticka (vidi se u donjem delu programa, u logu)
- gore levo klikni duplo na slovo koje oznacava particiju, tj. tvoj USB stick
- dole kraj sata ce se pojaviti poruka da smes da izvadis USB stick iz kompa
- ne gasi program, vec ubaci sledeci USB stick i za njega isto sacekaj par sekundi, i tako redom za sve stickove, MP3 plejere, mobilni
- zapamti kojim redom su ubacivani stickovi
Kada sve to zavrsis, log u donjem delu programa ce sadrzati sve podatke koji su meni potrebni da bih video koji stick je zarazen.
Klikni desnim dugmetom misa na log/izvestaj i odaberi Save log.
Automatski ce se otvoriti Notepad i u njemu izvestaj.
Iskopiraj mi taj izvestaj ovde na forum.
------------------------------------------------------------
Preuzmi gmer.zip sa ovog linka i sačuvaj na Desktopu.
Raspakuj ga u neki folder.
Dupli klik na gmer.exe za početak: Izaberi Rootkit/Malware Tab na vrhu.
Klikni na Scan.
Kada je skeniranje završeno, klik na Copy dugme ispod - ovo će sačuvati rezultate skeniranja u Clipboard.
Iskoristi opciju Paste u Notepad-u da bi to prebacio u tekst. Snimi taj tekst iz Notepada kao file1.txt.
Ponovi ovo isto sa Autostart Tab-om. Snimi taj tekst iz Notepada kao file2.txt.
Iskoristi opciju Prikači fajl ispod polja za pisanje poruke na forumu, i prikači nam ovde ta dva fajla koja smo malopre snimili
|
|
|
|
|
|